Evidence brief library, page 11

Desk-reviewed evidence for staffing decisions

Compare roles, controls, and onboarding decisions with source context and practical operating guidance kept visibly separate.

251 briefsSource listsBuyer controls
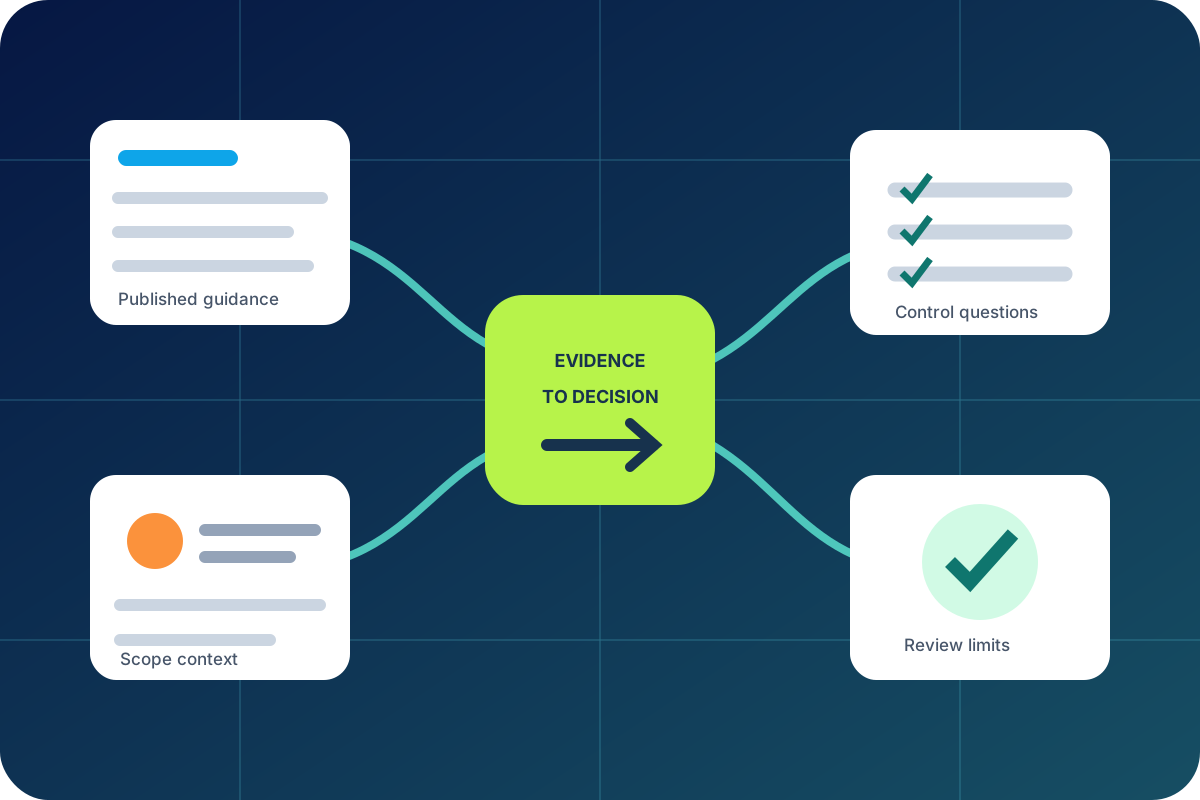
Published sources connected through an evidence map to a bounded operating decision

Research library

Read the evidence, limits, and operating questions together

These are desk reviews, not claims of original empirical research. Source counts describe each bibliography and do not prove provider performance.

Evidence brief illustration for Call Recording Governance: A Research Brief

Hiring controls

Call Recording Governance: A Research Brief

Recordings can contain personal, payment, and authentication data. NIST Privacy Framework and PCI DSS materials support purpose limitation, controlled access, retention decisions, and protection of sensitive data; a recording policy must also account for jurisdiction-specific rules.

6 min read10 sources
Read brief
Evidence brief illustration for Call Center Phishing Escalation: A Research Brief

Scope benchmarks

Call Center Phishing Escalation: A Research Brief

CISA describes phishing as a social-engineering risk, and NIST identity guidance supports independent verification rather than trusting the channel that made the request. Agents need a pause-and-escalate rule, not a mandate to investigate intent.

6 min read10 sources
Read brief
Evidence brief illustration for Payment Call Handling Controls: A Research Brief

Workflow design

Payment Call Handling Controls: A Research Brief

PCI DSS is designed to protect payment account data and its document library provides the governing standard and supporting guidance. Outsourcing a call task does not remove the merchant's responsibility to define the card-data environment and approved handling method.

6 min read10 sources
Read brief
Evidence brief illustration for Outbound Appointment Calls: A Research Brief

Hiring controls

Outbound Appointment Calls: A Research Brief

The FTC Telemarketing Sales Rule and FCC consumer guidance show why consent, identification, time-of-day, do-not-call, and opt-out handling must be explicit in outbound workflows. The sources do not create one universal script for every jurisdiction.

6 min read10 sources
Read brief
Evidence brief illustration for Call Center QA Sampling: A Research Brief

Scope benchmarks

Call Center QA Sampling: A Research Brief

ISO 18295 links contact-center performance to defined processes and results. NIST risk frameworks support repeatable measurement and improvement, but neither source endorses a single sample size or scorecard.

6 min read10 sources
Read brief
Evidence brief illustration for Call Center Incident Response: A Research Brief

Workflow design

Call Center Incident Response: A Research Brief

NIST CSF 2.0 organizes cybersecurity work around Govern, Identify, Protect, Detect, Respond, and Recover. That structure supports a small queue-level incident card and clear ownership without asking frontline agents to perform security investigations.

6 min read10 sources
Read brief
Evidence brief illustration for Call Center Schedule Handoffs: A Research Brief

Hiring controls

Call Center Schedule Handoffs: A Research Brief

The FLSA establishes U.S. federal wage-and-hour requirements for covered workers; it is not a universal staffing calculator and does not answer every cross-border employment question. A schedule therefore needs both service coverage logic and a responsible employer or client review.

6 min read10 sources
Read brief
Evidence brief illustration for Call Center Script Change Control: A Research Brief

Scope benchmarks

Call Center Script Change Control: A Research Brief

NIST frameworks emphasize governance, documented controls, and continuous improvement. A script change can alter privacy, payment, consent, or escalation behavior, so publishing wording without an owner and effective date creates avoidable risk.

6 min read10 sources
Read brief
Evidence brief illustration for Call Center Metrics That Managers Can Use: A Research Brief

Workflow design

Call Center Metrics That Managers Can Use: A Research Brief

Contact-center standards and risk frameworks support outcome-based measurement, but metric definitions must be local and transparent. A number without its denominator, time window, channel, or exclusion rule can produce a misleading operating decision.

6 min read10 sources
Read brief
Evidence brief illustration for Call Center Customer Data Retention: A Research Brief

Scope benchmarks

Call Center Customer Data Retention: A Research Brief

NIST privacy guidance treats data processing as a governed lifecycle, while PCI DSS requires protection of payment account data. Neither source supplies a blanket retention period for every support operation; the client must define purpose, legal, and contractual requirements.

6 min read10 sources
Read brief

Desk-review method and limits

Each brief lists the sources consulted, makes assumptions visible, and separates sourced facts from editorial recommendations. A listed source count describes the bibliography. It is not a claim of original empirical research, a legal opinion, or proof that one provider will achieve a particular result.