
Hiring controls
Call Center Sensitive Field Exposure: A Research Brief
Sensitive information can spread through notes, recordings, exports, and review samples even when the original customer contact was permitted.
Read briefEvidence brief library, page 8
Compare roles, controls, and onboarding decisions with source context and practical operating guidance kept visibly separate.
Research library
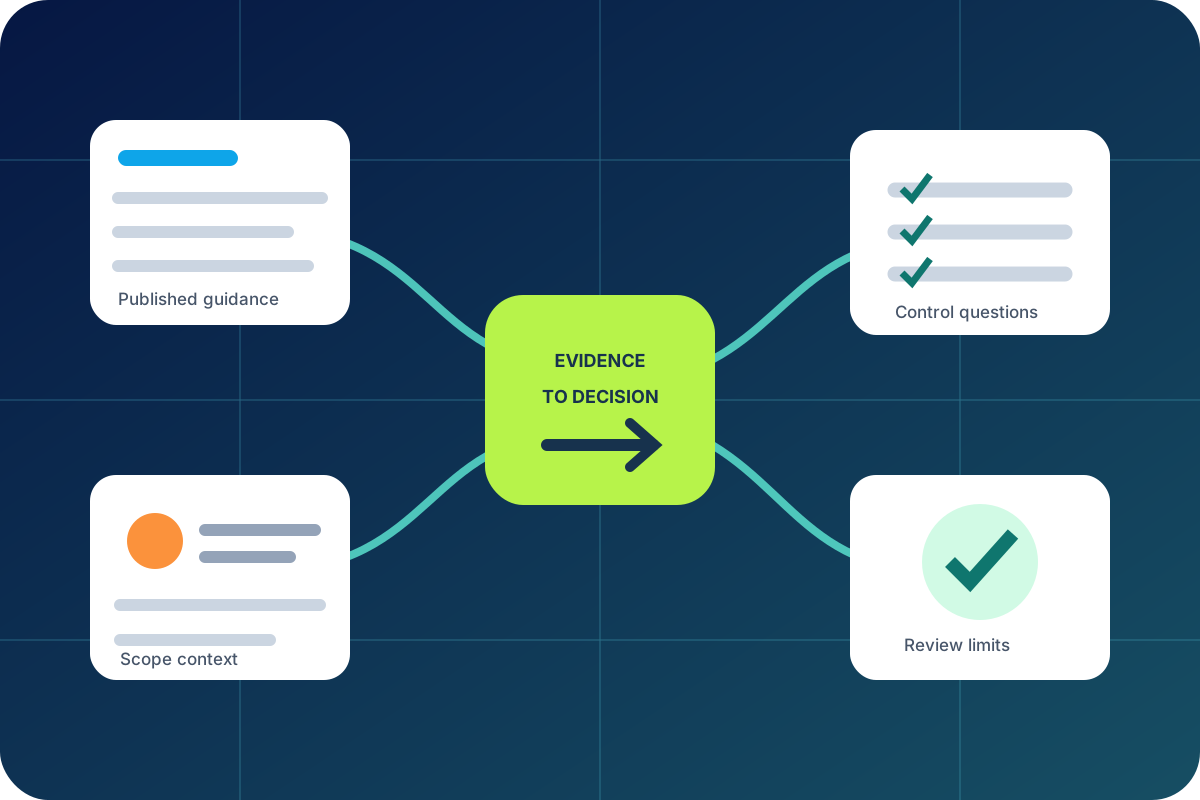
These are desk reviews, not claims of original empirical research. Source counts describe each bibliography and do not prove provider performance.
Hiring controls
Sensitive information can spread through notes, recordings, exports, and review samples even when the original customer contact was permitted.
Read brief
Scope benchmarks
Outbound contact records need purpose, channel, source, timing, opt-out state, and an owner who can resolve uncertainty before another attempt.
Read brief
Workflow design
Callback reliability depends on preserving the customer's local window, the source of the time-zone value, and the owner of a missed promise.
Read brief
Hiring controls
A searchable answer is dependable only when its authority, scope, effective date, and conflict owner are visible.
Read brief
Scope benchmarks
Role changes require a timed access review and an owned handoff so stale permissions and orphaned customer work do not persist.
Read brief
Workflow design
Payment exposure can persist in recordings, transcripts, notes, screenshots, and quality samples even after an interaction ends.
Read brief
Hiring controls
Accessibility continuity requires the next owner to understand the approved support need without making the customer repeat unnecessary sensitive context.
Read brief
Scope benchmarks
Notification preferences need separate purposes, channels, effective times, and owners when they move between service systems.
Read brief
Workflow design
A deadline communicated to a customer needs a clock, dependency record, accountable owner, and truthful fallback when feasibility changes.
Read brief
Hiring controls
Similarity across calls, messages, and tickets is not enough to merge records; linkage needs evidence, purpose, and an accountable owner.
Read brief
Scope benchmarks
Customer updates are safer when wording, timestamp, source facts, and next-update ownership agree.
Read brief
Workflow design
Complaint intake should preserve stated impact, verified facts, requested remedy, and the decision owner without turning allegations into findings.
Read brief
Hiring controls
Queue capacity is not just a headcount estimate: it is the amount of demand a defined team can handle while preserving customer access, safe decisions, and review ownership. ISO 18295 emphasizes customer-contact processes and results, while NIST governance guidance supports explicit risk ownership.
Read brief
Scope benchmarks
A transfer can protect a customer or simply move an unresolved problem between queues. ISO 18295 supports defined contact processes and outcomes; NIST guidance supports clear ownership and minimum necessary access during the handoff.
Read brief
Workflow design
A script change can alter customer promises, data handling, escalation triggers, and quality scoring at once. NIST governance principles support accountable change decisions, while ISO 18295 supports controlled processes and measurable results.
Read brief
Hiring controls
A fallback path should reduce lockout harm without becoming an easy bypass. NIST Digital Identity Guidelines and Zero Trust Architecture support contextual assurance, bounded authenticators, and an explicit authorization decision.
Read brief
Scope benchmarks
Service recovery works when the frontline response is empathetic but its authority is bounded. ISO 18295 emphasizes customer outcomes, while NIST governance supports documented ownership and exception handling.
Read brief
Workflow design
A handoff without timing evidence makes missed promises difficult to distinguish from late ownership. ISO 18295 supports defined processes and results, while NIST incident and governance guidance supports traceable responsibility.
Read brief
Hiring controls
An outsourced queue is safest when its customer types, channels, systems, decisions, and exclusions are explicit. NIST Zero Trust and Privacy Framework guidance support least privilege and purpose limitation; ISO 18295 supports defined service processes.
Read brief
Scope benchmarks
Language support improves access only when meaning, consent, sensitive terms, and ownership remain clear across the interaction. NIST privacy guidance supports minimum necessary disclosure, while ISO 18295 supports defined customer-contact processes.
Read brief
Workflow design
Escalation records need enough evidence for the next decision without becoming an uncontrolled copy of customer or payment data. NIST CSF 2.0 supports response ownership and recovery evidence; NIST Privacy Framework and PCI DSS materials support minimization and controlled handling.
Read brief
Hiring controls
Choosing voice, email, chat, or callback affects verification, privacy, response expectations, and escalation load. NIST identity and privacy guidance support contextual verification and purpose limitation; ISO 18295 supports defined channel processes and customer outcomes.
Read brief
Scope benchmarks
Appointment confirmation work combines customer data, schedule changes, and promises about time. NIST privacy guidance supports purpose limitation and controlled access, while ISO 18295 supports defined processes and measurable outcomes.
Read brief
Workflow design
Disposition codes shape reporting and the next action. A code set is useful only when each value has a clear meaning, owner, and review path. ISO 18295 emphasizes process and results, while NIST guidance supports traceable responsibility.
Read briefEach brief lists the sources consulted, makes assumptions visible, and separates sourced facts from editorial recommendations. A listed source count describes the bibliography. It is not a claim of original empirical research, a legal opinion, or proof that one provider will achieve a particular result.